Inside Japan's New Cyber Security Policy Division
Japan's Foreign Ministry has re-established a dedicated cyber division, as a wave of attacks on Japanese businesses pushes cybersecurity up the political agenda. It is a sign that cyber threats are now a matter of diplomacy, not just technical defence.
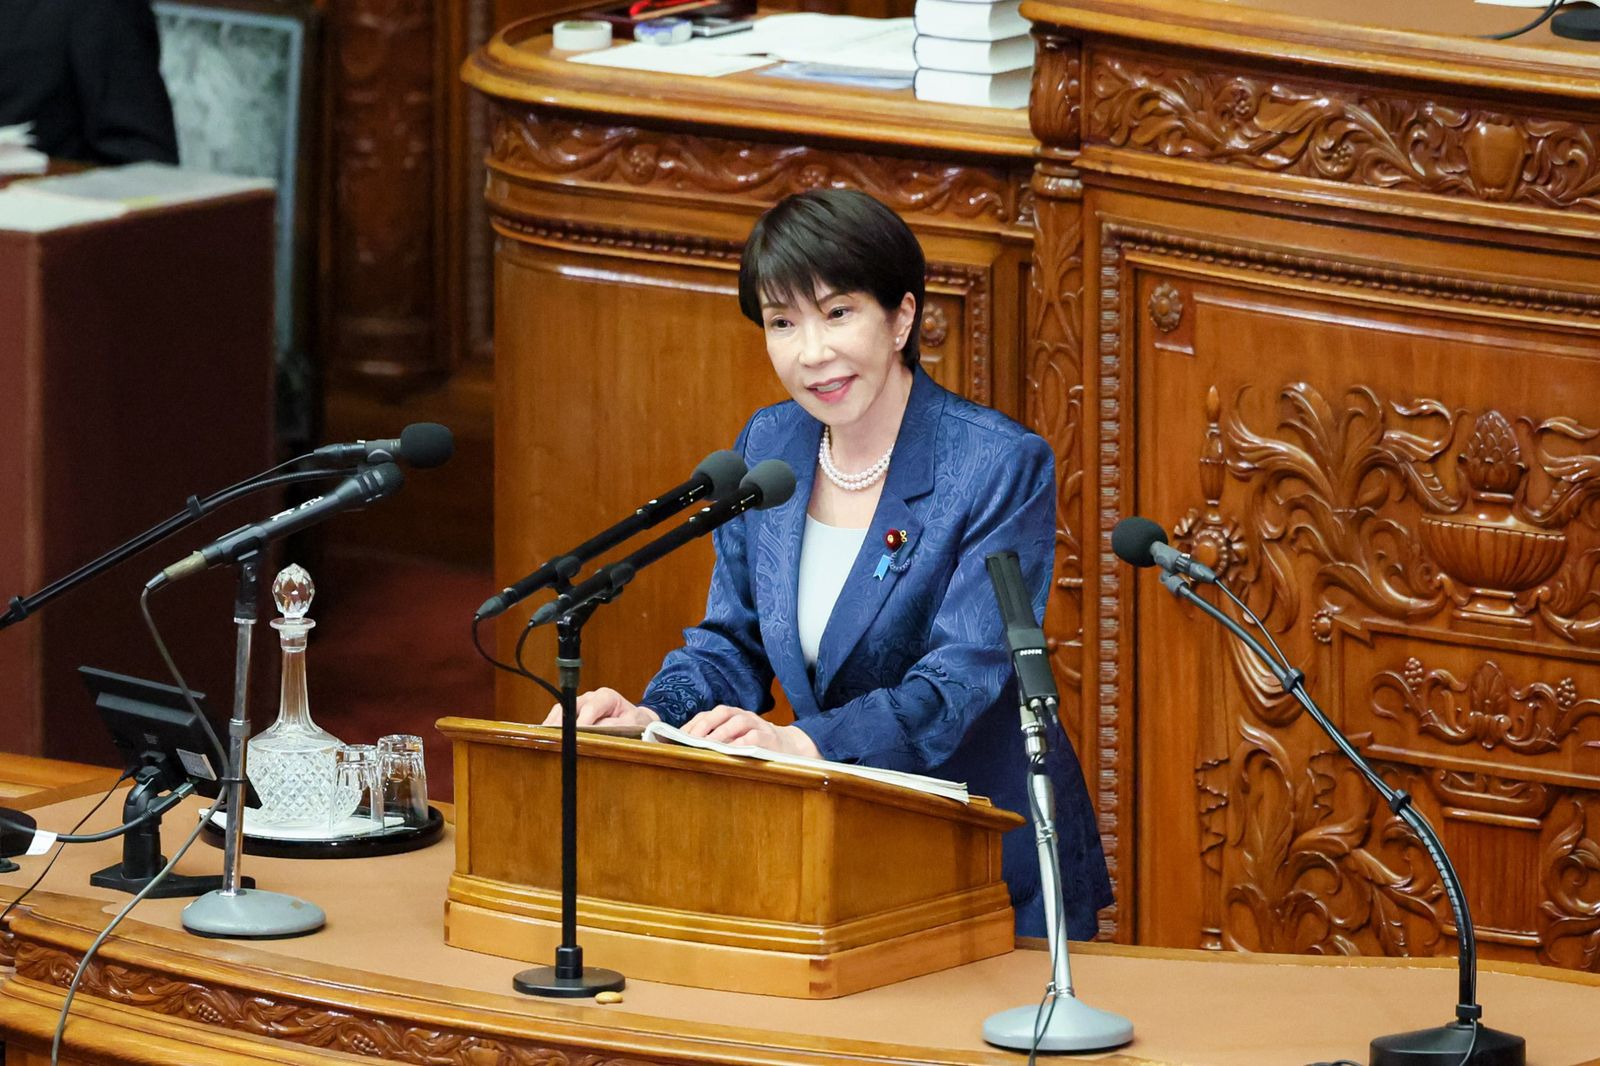
Prime Minister Sanae Takaichi. Photo: Prime Minister's Office of Japan / Cabinet Secretariat, Public Data License 1.0 (licence)
On 1 September 2026, Japan's Ministry of Foreign Affairs formally established a Cyber Security Policy Division, sitting within the National Security Policy Division of its Foreign Policy Bureau.1 The announcement received relatively modest international attention, particularly compared with the more visible cybersecurity investments being made by governments across Europe and North America. Yet the decision provides an important insight into how Japan is responding to the changing relationship between cybersecurity and international politics.
The division has been established to strengthen cooperation with international partners, contribute to the development of rules governing cyberspace and support diplomatic efforts to deter cyberattacks.1 Rather than concentrating on the technical work of defending networks, it is concerned with the international political environment in which cyber threats develop and governments respond to them.
The significance of this shift became particularly apparent in October, when Japanese Prime Minister Sanae Takaichi addressed a series of cyberattacks affecting major Japanese businesses.
Speaking during a House of Representatives session on 8 October, Takaichi acknowledged growing public concern about the exposure of personal information following several significant breaches.
"Numerous cyber-attacks involving personal data leaks have been reported, causing concern among the public," she said, according to The Japan News.2
The Prime Minister committed to strengthening Japan's cyber defences, particularly through the National Cybersecurity Office, while improving how the government collects and analyses information about attacks and communicates emerging threats to businesses.
Although Takaichi was referring to Japan's domestic cybersecurity response rather than the newly established Foreign Ministry division, the developments illustrate two connected priorities within the country's evolving approach. Japan is strengthening its ability to protect domestic infrastructure and businesses while developing the diplomatic relationships and international frameworks intended to support its security interests abroad.
A new division with a longer history
Although announced as a new division, Japan's latest initiative is not entirely new.
The Ministry of Foreign Affairs first established a Cyber Security Policy Division on 12 July 2016, at a time when governments were beginning to devote greater attention to the diplomatic implications of cyber threats. That original division was subsequently absorbed into the ministry's National Security Policy Division following an organisational reform.3,4
Ten years later, the ministry has decided that cybersecurity once again requires a dedicated organisational structure. According to reporting by Jiji Press, approximately 10 to 20 officials from the National Security Policy Division are concurrently serving in the re-established unit. The immediate change is therefore primarily about providing a clearer institutional focus for cyber diplomacy, rather than creating an entirely separate agency with a large new workforce.3
The distinction between the 2016 and 2026 announcements is particularly revealing. Both emphasise international cooperation and the rule of law, but the latest announcement places greater attention on international rule-making, deterring cyberattacks and strengthening cooperation with allies and partners.
This reflects a decade in which cybersecurity has moved much further into mainstream national security and foreign policy discussions. Governments increasingly recognise that the consequences of cyber incidents can extend beyond the organisations directly targeted, affecting economic stability, diplomatic relationships and international security.
For Japan, restoring the division provides a dedicated institutional structure through which these issues can be addressed internationally.
Why Japan is strengthening its approach
Japan's decision comes against a backdrop of growing concern about cyber threats affecting government institutions, major businesses and critical infrastructure. Like many advanced economies, Japan depends on complex digital systems supporting manufacturing, finance, transport, communications and public services.
The potential consequences of disruption extend well beyond the organisations directly targeted. An attack against a major manufacturer can affect international supply chains, while an incident involving transport or communications infrastructure can have implications for economic activity and public confidence.
The scale of the challenge became particularly visible in October 2026, when several major Japanese companies disclosed significant cybersecurity incidents.
Convenience store operator Lawson reported that unauthorised access to its Lawson ID accounts had exposed personal information relating to approximately 2.15 million users, around a tenth of its members, including names and contact details. A separate breach of its app reservation system exposed further records, some with partial card numbers.5,7
Meanwhile, Daiichikosho, which operates the Big Echo karaoke chain, warned that approximately 8.72 million pieces of personal data relating to customers and employees might have been compromised following a malware infection on a computer at an external contractor.6,7
These incidents prompted an interministerial meeting, with officials seeking to strengthen warnings to businesses and encourage improvements in basic cybersecurity practices.
The National Cybersecurity Office told ministries to pass instructions on to local governments and businesses: keep security protections up to date, use strong passwords and strengthen security across supply chains.8
The incidents also exposed an important limitation in national cybersecurity strategies. While governments often concentrate attention and resources on protecting critical infrastructure, attackers can also target ordinary commercial businesses, suppliers and service providers whose operations fall outside the most tightly regulated sectors.
This creates a broader national security challenge, particularly in economies where businesses operate through interconnected digital systems and international supply chains.
There is also a geopolitical dimension.
Japan occupies an important position in the Indo-Pacific, where competition between major powers, concerns about regional security and questions surrounding technological dependence have become increasingly prominent.
The country maintains close security relationships with the United States and other international partners, while its economic interests depend heavily on regional stability and the continued operation of international trade and technology networks.
Cybersecurity has consequently become closely connected to Japan's wider strategic interests. The ability to respond to incidents domestically remains essential, but so too does the ability to cooperate internationally, establish common expectations of responsible behaviour and influence the development of rules governing cyberspace.
What will the division actually do?
The division's responsibilities are primarily diplomatic, distinguishing it from operational cybersecurity organisations tasked with monitoring threats, responding to incidents or protecting government infrastructure.
Its work is expected to concentrate on several interconnected areas, including international rule-making, cooperation with partner governments, deterrence and cybersecurity capacity building.
An important element is Japan's support for the application of international law in cyberspace. International discussions have increasingly addressed how established legal principles apply to cyber operations, including questions about sovereignty, state responsibility and acceptable behaviour.
Japan wants to participate actively in these discussions, including through the United Nations and other multilateral institutions. Its position is that international law applies in cyberspace11 and that cooperation between governments is essential to establishing stability and reducing the risks associated with malicious activity.
Another responsibility involves strengthening relationships with allies and other partners. Cyber threats frequently cross national borders, making cooperation important for sharing information, coordinating diplomatic responses and developing common policy positions.
Japan already participates in numerous bilateral and multilateral cybersecurity discussions, including cooperation involving the United States, the European Union, Australia and countries across the Indo-Pacific.
The division is expected to support this existing diplomatic network while giving cybersecurity greater institutional visibility within the Foreign Ministry.
Capacity building is another significant part of its mandate. Japan has been involved in supporting cybersecurity development in other countries, particularly across the Indo-Pacific. Such cooperation can involve training, institutional development and assistance in improving national cybersecurity preparedness.
These activities can contribute to regional security by strengthening the ability of partner countries to prevent, identify and respond to cyber incidents. They also provide a means for Japan to develop longer-term relationships with governments whose digital infrastructure is becoming increasingly important.
What makes Japan's approach different?
One of the most significant aspects of Japan's approach is the distinction between operational cybersecurity and cyber diplomacy.
In July 2025, Japan established the National Cybersecurity Office, replacing the previous National Center of Incident Readiness and Strategy for Cybersecurity. The new office was created to strengthen coordination across government and oversee national cybersecurity policy, including monitoring and analysing malicious activity affecting government information systems.9
The Cyber Security Policy Division serves a different purpose. Located within the Ministry of Foreign Affairs, its focus is on the international relationships, diplomatic negotiations and policy frameworks surrounding cybersecurity.
This separation is important because international cybersecurity cannot be managed exclusively through domestic institutions. Governments may develop increasingly sophisticated defensive capabilities, but they still need diplomatic mechanisms for communicating with other states, addressing disagreements and cooperating on shared threats.
Japan's institutional arrangements therefore recognise two complementary requirements. The country needs the ability to protect its own systems and respond to malicious activity, while also participating in the international discussions that influence how governments behave in cyberspace.
The division itself is not unique internationally. The United States and several European countries have established dedicated cyber diplomacy functions, recognising the importance of representing national cybersecurity interests through foreign policy institutions.
What makes Japan's recent decision interesting is its place within a wider restructuring of national cybersecurity policy, combined with the country's strategic position in the Indo-Pacific and a renewed emphasis on diplomatic engagement.
Japan is strengthening domestic cyber coordination, developing a more active approach to cybersecurity and giving renewed institutional attention to international cyber diplomacy. These developments are taking place within a relatively short period, illustrating the increasing prominence of cybersecurity within the country's national policy agenda.
Cyber diplomacy and deterrence
The establishment of the division also needs to be understood alongside Japan's changing approach to cyber deterrence.
Historically, much of the public discussion surrounding cybersecurity has focused on protecting systems against attacks. Increasingly, governments are also examining how they can identify threats earlier, disrupt malicious activity and discourage future attacks.
Japan has been developing what it describes as an active cyber defence approach. Legislation passed in May 2025 created a framework for strengthening its response capabilities, including measures intended to prevent serious harm from cyberattacks. Its key provisions took effect on 1 October 2026.10
These developments form part of a broader shift in Japanese security policy, reflecting concerns about the limitations of responding only after attacks have occurred.
The Foreign Ministry's Cyber Security Policy Division does not itself represent an offensive cyber capability. However, it has a role in the wider diplomatic environment surrounding deterrence.
Attributing malicious activities to particular actors, coordinating responses with other governments and developing international expectations of acceptable behaviour are all ways in which diplomatic institutions can contribute to cybersecurity.
This introduces an important distinction between possessing technical capabilities and establishing the political conditions in which those capabilities are used.
A government may be able to identify or disrupt malicious cyber activity, but decisions about international responses, escalation and the interpretation of legal obligations can involve complex diplomatic considerations.
By providing a dedicated structure for these discussions, Japan is seeking to connect its domestic security priorities more closely with its international relationships.
The importance of the Indo-Pacific
Japan's geographical and political position gives its cybersecurity diplomacy particular relevance.
The Indo-Pacific is home to some of the world's most significant digital economies, major technology manufacturers and important international communications infrastructure. It is also a region in which countries have different levels of cybersecurity preparedness and sometimes differing positions on the governance of cyberspace.
Japan has been developing relationships with regional partners through cybersecurity training and cooperation programmes, including initiatives involving ASEAN countries.
Such activities are not limited to addressing immediate technical vulnerabilities. They can also strengthen diplomatic relationships, encourage greater compatibility between national cybersecurity policies and provide smaller countries with opportunities to participate more effectively in international discussions.
For Japan, this creates an additional dimension of foreign policy. Supporting cybersecurity capabilities abroad may also contribute to the resilience of regional infrastructure and supply chains on which its own economy depends.
However, capacity-building initiatives also raise questions about whose priorities guide international cybersecurity cooperation. Recipient countries may have different economic, political and security requirements from those of the states providing assistance.
The effectiveness of Japan's approach will therefore depend partly on how partnerships are developed, whether programmes respond to local needs and how participating countries are involved in defining their own cybersecurity priorities.
This dimension is particularly important in an international environment where technological cooperation increasingly overlaps with strategic competition.
From technical security to geopolitical influence
The broader significance of Japan's Cyber Security Policy Division lies in what its establishment tells us about the changing role of cybersecurity within international relations.
For many years, cybersecurity was frequently approached as a specialist technical discipline. Although international security concerns were always present, responsibility for managing digital threats often sat primarily with technical agencies, intelligence organisations or defence institutions.
That institutional landscape has gradually changed.
Cybersecurity now influences trade negotiations, economic security, technology policy and diplomatic cooperation. Questions surrounding digital infrastructure, supply chains, artificial intelligence and cross-border information flows can all carry geopolitical consequences.
Governments are consequently investing not only in defensive technologies, but also in the institutions needed to represent their interests internationally.
Japan's decision to restore a dedicated cyber diplomacy division reflects this development. It recognises that the future of cybersecurity will be shaped as much by diplomatic relationships and international rules as by developments in technology.
There are nevertheless limitations to what a relatively small diplomatic division can achieve. Its effectiveness will depend on coordination with other Japanese institutions, the influence Japan can exercise in international negotiations and the willingness of partner governments to cooperate.
It also remains to be seen whether the division will produce substantive changes in Japan's international cybersecurity activities or principally improve the organisation and visibility of work already taking place.
The institutional separation between domestic security and foreign policy could help clarify responsibilities, although effective cooperation between the different organisations will remain essential.
Why this matters beyond Japan
Japan's decision offers an illustration of how cybersecurity governance is evolving internationally.
The establishment of a dedicated diplomatic division does not eliminate cyber threats, nor does it resolve the disagreements that exist between states over security, sovereignty and the regulation of technology. It does, however, provide an institutional mechanism through which those issues can be addressed.
For other governments, the development raises questions about how cybersecurity responsibilities should be distributed between foreign ministries, national cybersecurity authorities, defence organisations and the private sector.
It also highlights the growing importance of international engagement for countries seeking to influence the future governance of cyberspace.
Japan is not starting from nothing. Its Foreign Ministry has been engaged in cyber diplomacy for more than a decade, and the re-established division builds on existing programmes, partnerships and policy commitments.
What has changed is the wider environment in which those activities take place.
The recent attacks against Japanese businesses, alongside the Prime Minister's commitment to stronger national defences, demonstrate why cybersecurity has become an increasingly prominent domestic political issue. At the same time, the restoration of a dedicated diplomatic division shows that Japan also considers international cooperation and rule-making essential parts of its response.
Cybersecurity is increasingly connected to economic resilience, regional security and international political influence. By restoring the Cyber Security Policy Division, Japan is giving greater organisational attention to these connections.
The development may appear relatively modest in institutional terms, particularly when compared with larger investments in technical cybersecurity capabilities. Its significance lies in the recognition that protecting a country's digital interests increasingly requires engagement beyond its own borders.
For Japan, cybersecurity is becoming not only a question of defending networks, but also one of shaping the international relationships and rules under which those networks operate.
Corrections: none. If you spot an error, tell us and we will correct it openly.